Posts

Showing posts with the label web

somebody's been php'in ... - Dangers of source code disclosure for web site security

Image
Menzis: somebody's been php'in ... A `$` is not always a positive thing to see, especially in the title of your favourite website not be rendered, but a value replaced where this variable $name appears). So, hopefully the general health of the website is otherwise acceptable... More seriously, such  Source code  disclosure  ('code leak thru') bugs can indicate security faults : when code fails to render, it may inadvertently leak algorithm details or even worse connection strings and other sensitive details that a hacker may exploit...
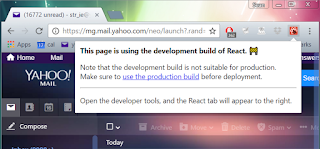
Yahoo: still learning ReactJS ... - Deploying a dev build to a live website

Image
For frontend web developers, there is a handy Chrome plugin, to inspect the state of the ReactJS website. However, a disadvantage is of course that just about any other ReactJS dev can also inspect your public website. If you happen to have deployed using a *dev* (internal, not really optimized for production) build, then this can be detected by your users. Unfortunately Yahoo Mail! had this issue for a while (but it seems OK now)... Word to the wise: sanity check your production software now and then!